TBW / AI solutions
Private AI
Keep sensitive workflows inside an intentional trust boundary.
The business problem
Sending every prompt and document to a public endpoint may not fit enterprise data policy.
What TBW provides
On-premises or private-cloud design
Designed around your environment, requirements and operating constraints.
Approved model access and retrieval
Designed around your environment, requirements and operating constraints.
Network segmentation and operating plan
Designed around your environment, requirements and operating constraints.
Architecture and workflow
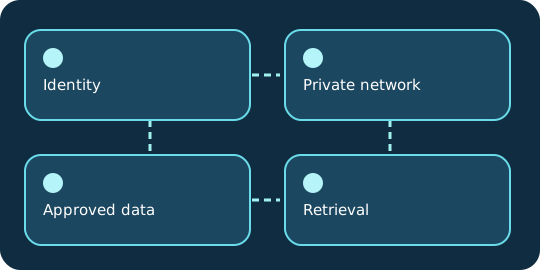
- Identity
- Private network
- Approved data
- Retrieval
- Model
- Audited answer
Architecture is selected after reviewing the actual data, identity, operations and integration boundaries. See enterprise integration →
A representative workflow
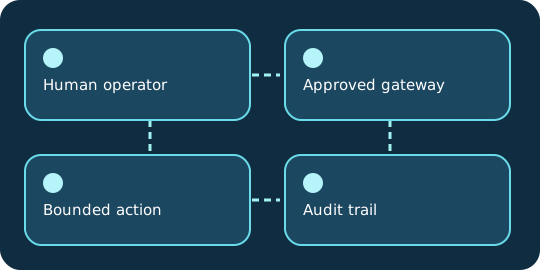
An analyst asks a question through an approved gateway; source documents remain in the private environment. This illustration describes a design pattern, not a deployed customer case study.
Technologies involved
Technology categories below are examples for architecture discussion, not a vendor partnership or an assertion that every tool is deployed.
Implementation methodology
- Discover requirements
- Assess data and access
- Architect and prototype
- Integrate and secure
- Validate and operate
Security and governance
Classify data; authenticate users; apply least-privilege model and tool access; review retention and residency; test prompt injection and unsafe retrieval; log meaningful decisions; require human approval for sensitive actions. The controls and assurance required depend on your environment.
Related services
Frequently asked questions
Does private AI mean no cloud?
Not necessarily. A private-cloud deployment can still use cloud infrastructure; residency and provider access must be verified contractually and technically.
How are access and data boundaries defined?
Start with a data inventory, named owners and role-based permissions. Test the actual flow before production and revisit access as systems change.
What is the next step?
Bring a bounded use case, constraints and existing architecture to a consultation. No deployment or result is assumed before assessment.
Plan the next architecture decision
Discuss the workload, data boundaries, integrations and operational ownership with TBW.